Resilient Security Framework for Enterprise AI Workflows
Modern enterprise operations rely heavily on automated intelligence pipelines and language models. However, bringing machine learning into core business workflows creates novel attack vectors that legacy perimeter defenses fail to isolate. Our Enterprise AI Security Management framework establishes strict protocol boundaries around inference endpoints, training datasets, and automated agent swarms.
By coupling granular role-based access controls with continuous cryptographic validation of data streams, organizations ensure that corporate intellectual property remains contained. Systems automatically identify drift, adversarial prompt patterns, and anomalous API payloads in real time without introducing latency into production systems.
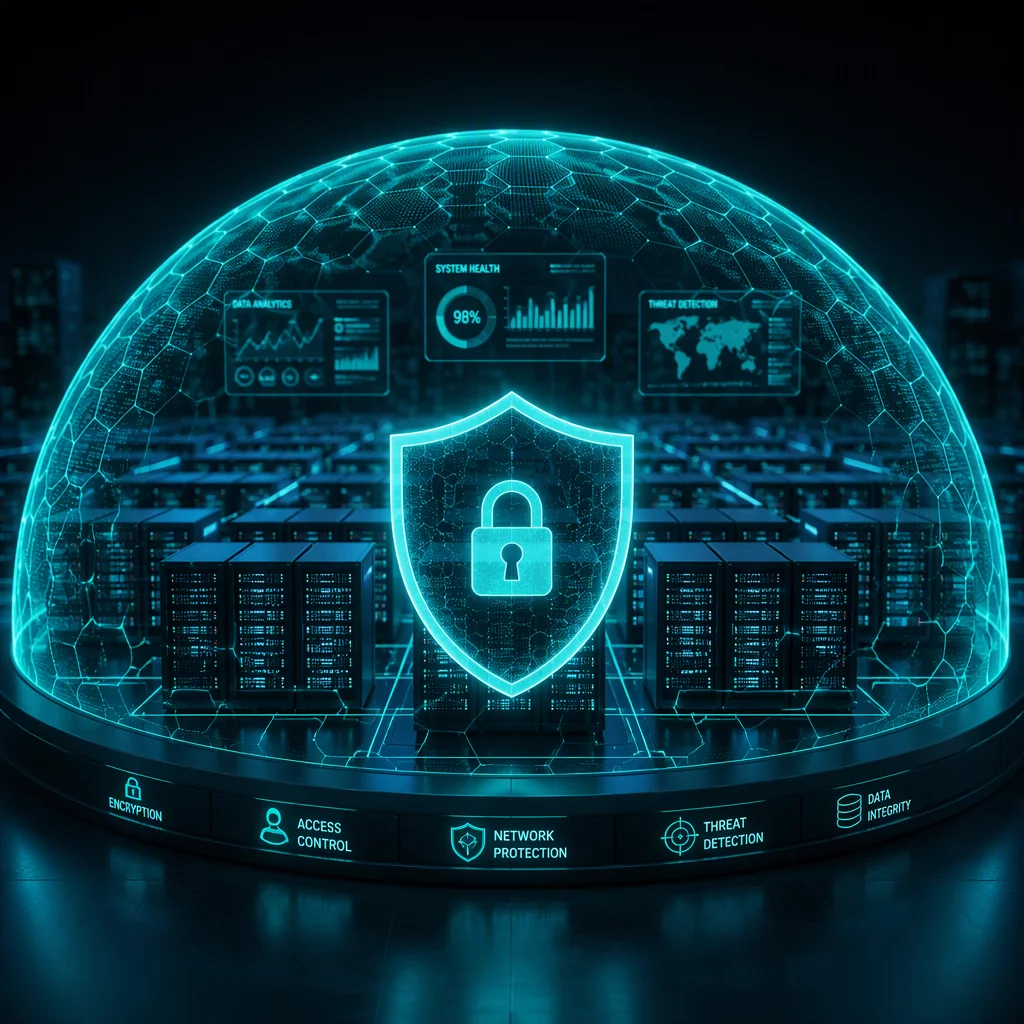
Security Architecture Specifications
Core Capabilities and Threat Prevention
Securing production intelligence requires multidimensional defenses that address every phase of the algorithmic lifecycle, from data ingestion to downstream automation.
-
Automated Prompt & Payload Sanitization
Inspect incoming model requests and contextual data embeddings to prevent indirect injection attacks, exfiltration commands, and unauthorized execution routines.
-
Granular Data Isolation & Masking
Automatically redact personally identifiable information and proprietary figures before inputs reach external or internal model backbones.
-
Comprehensive Drift and Anomaly Triangulation
Detect subtle performance degradation, model poisoning, or malicious output generation using automated baseline comparisons.